Introduction
Artificial Intelligence is moving beyond answering questions and generating content. With Agentic AI, organizations can build systems that plan tasks, interact with applications, retrieve information, and support multi-step business workflows.
These capabilities create new opportunities for enterprise operations. However, they also introduce important responsibilities.
When an AI agent interacts with business systems or performs actions, organizations need to understand what it can access, what it is allowed to do, and how its activities are monitored.
This is where AI governance becomes essential.
AI governance should not be treated as a final security step. It must be considered from the beginning of Agentic AI design and implementation.
1. What Is AI Governance?
AI governance refers to the policies, processes, technical controls, and responsibilities that guide how Artificial Intelligence systems are developed, deployed, and managed.
For enterprise AI systems, governance helps organizations establish clear rules around:
- Data access and privacy.
- Security and user permissions.
- AI system behavior and limitations.
- Human oversight and approval.
- Monitoring and evaluation.
- Accountability and auditability.
- Regulatory and organizational requirements.
A well-defined governance approach helps organizations use AI responsibly while maintaining control over business operations.
2. Why Agentic AI Requires Stronger Governance
Traditional AI applications often respond to user questions or generate content. Agentic AI systems can go further by interacting with external tools and supporting actions across multiple systems.
For example, an enterprise agent may be designed to retrieve customer information, prepare a report, create a service request, or initiate a workflow.
Without suitable controls, these capabilities may introduce risks.
Unauthorized Access: An agent may attempt to retrieve information beyond the user’s permitted access.
Incorrect Actions: An agent may select an incorrect tool or perform an unintended operation.
Data Exposure: Sensitive information may be exposed through prompts, responses, logs, or connected services.
Unreliable Outputs: AI-generated decisions or recommendations may contain errors.
Limited Accountability: Organizations may find it difficult to understand why an agent performed a particular action if monitoring is inadequate.
These challenges make governance an important part of enterprise Agentic AI architecture.
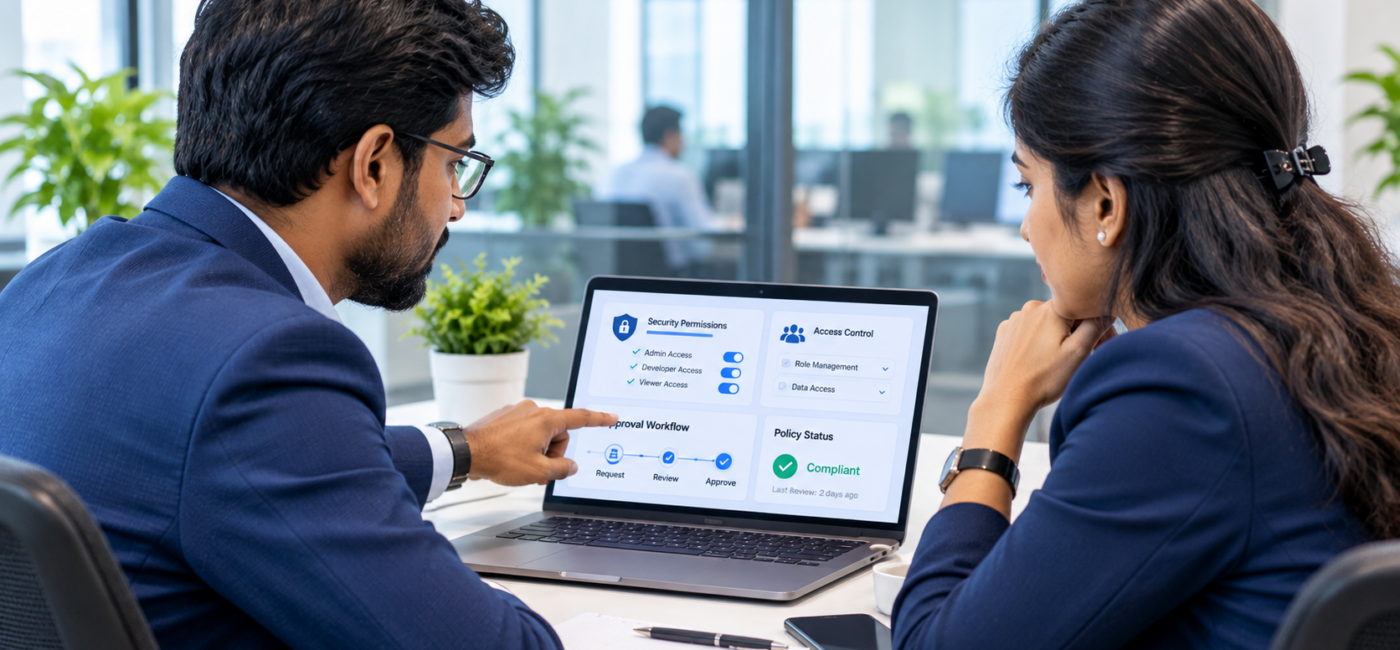
3. Define Clear Permissions for Every AI Agent
AI agents should operate within clearly defined boundaries.
Organizations should determine which information, tools, and systems each agent is permitted to access.
Important controls include:
Role-Based Access: Give agents access according to their assigned responsibilities.
Least-Privilege Access: Provide only the permissions required to complete the intended task.
Tool Restrictions: Allow agents to use only approved tools and functions.
Data Access Policies: Ensure that access to enterprise information follows organizational permissions.
Action Boundaries: Define which operations an agent can perform independently and which require additional approval.
These controls help reduce unnecessary access and limit the impact of unexpected agent behavior.
4. Keep Human Approval in Important Decisions
Not every action should be executed automatically.
For sensitive or high-impact workflows, organizations should include human review and approval before an AI agent proceeds.
For example:
- Financial transactions may require authorized approval.
- Changes to important business records may need human confirmation.
- External communications may require review before sending.
- Critical operational decisions may need employee validation.
- Access to sensitive information may require additional authorization.
Human-in-the-loop controls help organizations maintain accountability while still benefiting from automation.
The level of human involvement should depend on the business impact and risk associated with each action.
5. Protect Enterprise Data and Systems
Agentic AI systems often connect with internal applications, databases, APIs, and knowledge repositories.
These connections must be designed with security in mind.
Organizations should consider:
Authentication: Verify the identity of users, agents, and connected services.
Authorization: Check whether the requested operation is permitted.
Encryption: Protect sensitive information during transmission and storage.
Secure API Integration: Use appropriate credentials, permissions, and access policies.
Sensitive Data Protection: Avoid exposing confidential information unnecessarily through prompts or responses.
Credential Management: Store and manage access credentials securely rather than embedding them directly in application code.
Security controls should apply throughout the entire AI workflow, including retrieval, reasoning, tool usage, and output generation.
6. Monitor and Evaluate Agent Behavior
Deploying an AI agent is not the end of the implementation process.
Organizations need visibility into how agents behave, which tools they use, and whether their actions follow defined policies.
Monitoring and evaluation should include:
- Recording relevant agent activities and tool interactions.
- Tracking errors and unexpected behavior.
- Evaluating response quality and task completion.
- Monitoring access attempts and permission violations.
- Reviewing important actions and approval decisions.
- Testing system behavior when models, tools, or data sources change.
Regular evaluation helps organizations identify issues and improve system reliability over time.
7. Prevent Risks from Untrusted Inputs and Connected Tools
Agentic AI systems may receive information from users, documents, external websites, and connected applications.
Some of these sources may contain incorrect, misleading, or malicious instructions.
Organizations should consider risks such as prompt injection, unsafe tool usage, and unexpected data exposure.
Useful safeguards include:
- Treating external content as untrusted input.
- Validating information before using it in important workflows.
- Restricting tools to approved operations.
- Separating instructions from retrieved content.
- Applying output validation where necessary.
- Requiring approval for sensitive actions.
- Testing systems against realistic security scenarios.
These safeguards help reduce the risk of unintended behavior when agents interact with external information and enterprise systems.
8. Build Governance into the AI Development Lifecycle
Governance should be included at every stage of an Agentic AI project.
Planning and Strategy
Identify the business purpose, intended users, potential risks, and acceptable levels of automation.
Architecture and Design
Define agent responsibilities, data access, tool permissions, security requirements, and approval processes.
Development and Testing
Validate agent behavior, evaluate outputs, test integrations, and assess security controls.
Deployment
Introduce monitoring, access policies, operational procedures, and human oversight.
Continuous Improvement
Review performance, investigate issues, update policies, and evaluate system changes.
This approach helps organizations build governance into the system rather than relying on manual checks after deployment.
9. Moving Toward Responsible Enterprise Agentic AI
Successful enterprise AI adoption requires a balance between innovation, business value, and risk management.
Organizations should begin with clearly defined use cases and establish governance requirements before expanding agent capabilities.
A practical approach includes:
- Start with limited and well-defined agent responsibilities.
- Establish access and permission boundaries.
- Introduce human approval for sensitive operations.
- Monitor agent activity and system performance.
- Evaluate security and reliability regularly.
- Expand capabilities based on validated results.
Governance should evolve as AI systems become more capable and business requirements change.
How Tritech Infosystems Supports Responsible Enterprise AI
Tritech Infosystems focuses on enterprise AI consulting and engineering, helping organizations explore practical AI solutions aligned with their business and technology requirements.
Our capabilities include:
AI Governance and Guardrails: Supporting responsible AI implementation through controls, monitoring, and evaluation.
Agentic AI Development: Engineering AI agents designed to support multi-step business workflows.
RAG and Knowledge Systems: Building solutions that retrieve and work with approved enterprise information.
Enterprise Integration: Connecting AI applications with business systems, APIs, and enterprise platforms.
AI Strategy and Consulting: Helping organizations evaluate AI opportunities and plan suitable implementation approaches.
By combining AI engineering with enterprise technology expertise, Tritech helps organizations consider security, governance, and operational requirements throughout the AI lifecycle.
Conclusion
Agentic AI offers